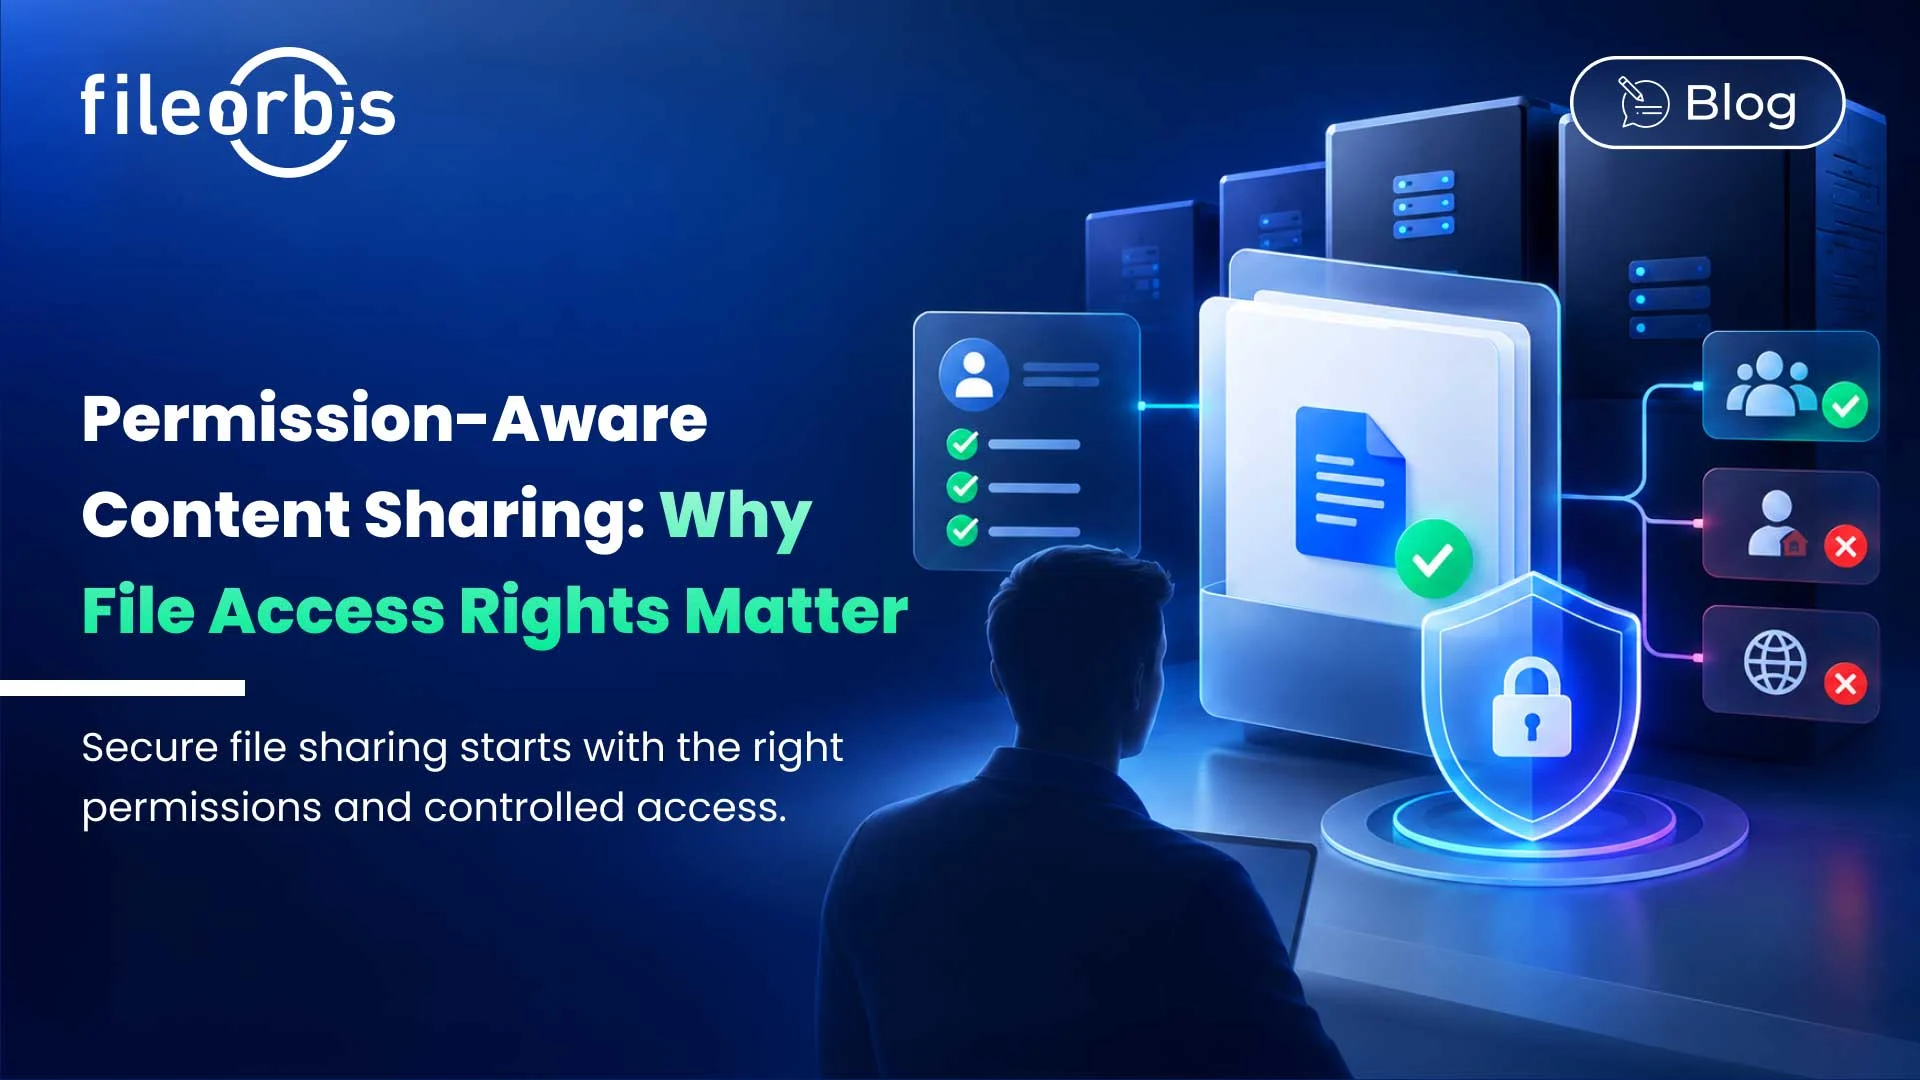
Permission-Aware Content Sharing: Why File Access Rights Matter
Having access permission to a file does not automatically mean having permission to share it.
An employee may legitimately access a financial report, confidential contract, or customer database. But does that authorization extend to forwarding it to an external partner or creating a public sharing link?
As enterprise files move across on-premises, cloud, and hybrid environments, traditional access controls alone may not provide sufficient oversight of how information is distributed.
Permission-aware content sharing addresses this challenge by aligning access rights with sharing authorization, organizational security policies, and content sensitivity.
What is Permission-Aware Content Sharing?
Permission-aware content sharing is a security approach that considers existing user access rights and organizational sharing policies to determine whether and how files can be distributed.
It addresses three questions:
- Who can access the file? Evaluate existing user and group permissions.
- Under what conditions? Apply policies based on content sensitivity, business requirements, and recipients.
- Who can share it? Verify authorization for internal or external distribution.
This approach supports least-privilege access while allowing authorized collaboration.
Why File Access Permissions Are Not Enough?
Traditional file permissions, including Active Directory and NTFS access control lists (ACLs), determine which users can access files and perform specific actions.
However, these permissions do not necessarily determine whether a user can distribute sensitive information outside the organization.
Consider a finance employee who needs to review a client financial report. Even if access is authorized, sharing that report with an external consultant could violate company policy.
Without appropriate sharing controls, organizations face risks such as:
- Excessive access: Users retain broader permissions than their responsibilities require.
- Uncontrolled external sharing: Sensitive files leave organizational boundaries without policy controls
- Unauthorized exposure: Confidential information reaches recipients without appropriate authorization.
- Limited visibility: Security teams struggle to monitor file distribution and investigate sharing activities.
These risks highlight the need to evaluate sharing actions independently of basic file access.
How Does Permission-Aware Content Sharing Work?
Effective permission-aware content sharing brings combines identity, existing permissions, policy enforcement, and content sensitivity.
Evaluate Existing Permissions
Access controls, such as NTFS ACLs and Active Directory, provide the foundation for determining which files users can access.
A permission-aware approach considers these rights before allowing sharing actions.
Validate Sharing Authorization
Sharing policies evaluate whether the requested distribution is permitted.
Key considerations include:
- User authorization to share the file
- Internal or external sharing destination
- Recipient identity and access rights
- Additional approval requirements
Enforce Content-Aware Policies
Access permissions alone do not indicate whether a document contains sensitive information.
Content-aware controls add another layer of protection by evaluating file classification, sharing context, and content.
Depending on organizational policies, controls may:
- Require approval for sensitive content
- Allow or block sharing
- Restrict downloads or external distribution
- Apply watermarking, encryption, or masking
- Record sharing activities through audit logging
Key Benefits of Permission-Aware Content Sharing
For enterprise security teams, permission-aware content sharing helps balance data protection with collaboration.
Key benefits include:
- Reduced data exposure: Limit unauthorized distribution of sensitive information.
- Controlled collaboration: Enable internal and external sharing under defined security policies.
- Enforce the principle of least privilege: Align sharing activities with approved access rights and business responsibilities.
- Consistent governance: Enforce centralized sharing policies across distributed file environments.
- Improved auditability: Maintain visibility into file access, policy decisions, and distribution.
How FileOrbis Helps
FileOrbis brings together permission governance, sensitive data classification, and content-aware sharing to help organizations control enterprise file distribution across existing storage environments.
Key capabilities include:
- Permission and Access Governance: Analyze file permissions, identify excessive access, and support least-privilege enforcement.
- Content-Aware Sharing: Inspect content and apply sharing controls based on sensitivity, context, and recipients.
- AI-Based Data Classification: Discover sensitive information and classify files to support policy decisions.
- Policy Enforcement: Apply approval workflows, watermarking, masking, blocking, and other security controls.
- Governance without Migration: Extend security controls across existing file servers, on-premises, and cloud storage without moving data.
- Audit Logging: Monitor file access, policy decisions, and sharing activities for greater accountability.
By combining these capabilities, FileOrbis helps organizations protect sensitive information and ensure secure enterprise collaboration.
In Summary
Secure file sharing requires more than controlling access to documents. Organizations should also govern how information is distributed and under which conditions.
Permission-aware content sharing combined with content-aware policy enforcement helps reduce unauthorized access, support secure collaboration, and strengthen access management.
FileOrbis enables these controls in existing enterprise data environments without requiring migration.
Frequently Asked Questions
What is permission-aware content sharing?
Permission-aware content sharing evaluates existing access rights and organizational policies to determine whether users are authorized to distribute files.
How does permission-aware content sharing reduce data exposure?
It combines access verification, content-aware policies, and sharing authorization to help prevent sensitive information from reaching unauthorized recipients
How are file access permissions different from sharing permissions?
Access permissions define what users can do with files on a storage environment. Sharing permissions determine whether and how those files can be distributed to others.
Gamze Karslı
Head of Marketing
Subscribe to our Newsletter
About FileOrbis
Aiming to manage the user and file relationship within an institutional framework, FileOrbis is constantly being developed in order to meet different industry and customer needs in terms of file management and sharing. Since 2018, FileOrbis continues to be developed with the excitement of the first day. FileOrbis focuses on high security, rich integration, ease of use and integrated management criteria.